↳
In-reply-to
»
Just a couple of shots from our trip to Bald Rock—finally got reception so I can share them!
⤋ Read More
Thank you, @prologic@twtxt.net, that looks really stunning! Seeing forests reaching beyond the horizon always amazes me. This does not exist around here. I also like those balancing rocks.
Keep ‘em coming. Looking forward to see more. But most importantly, enjoy your trip, mate! :-)
↳
In-reply-to
»
spring allergies suck
⤋ Read More
@kiwu@twtxt.net Oh, they absolutely do! There were waterfalls coming out of my nose. Luckily, it got much better over time. So, there might be chances for you, too.
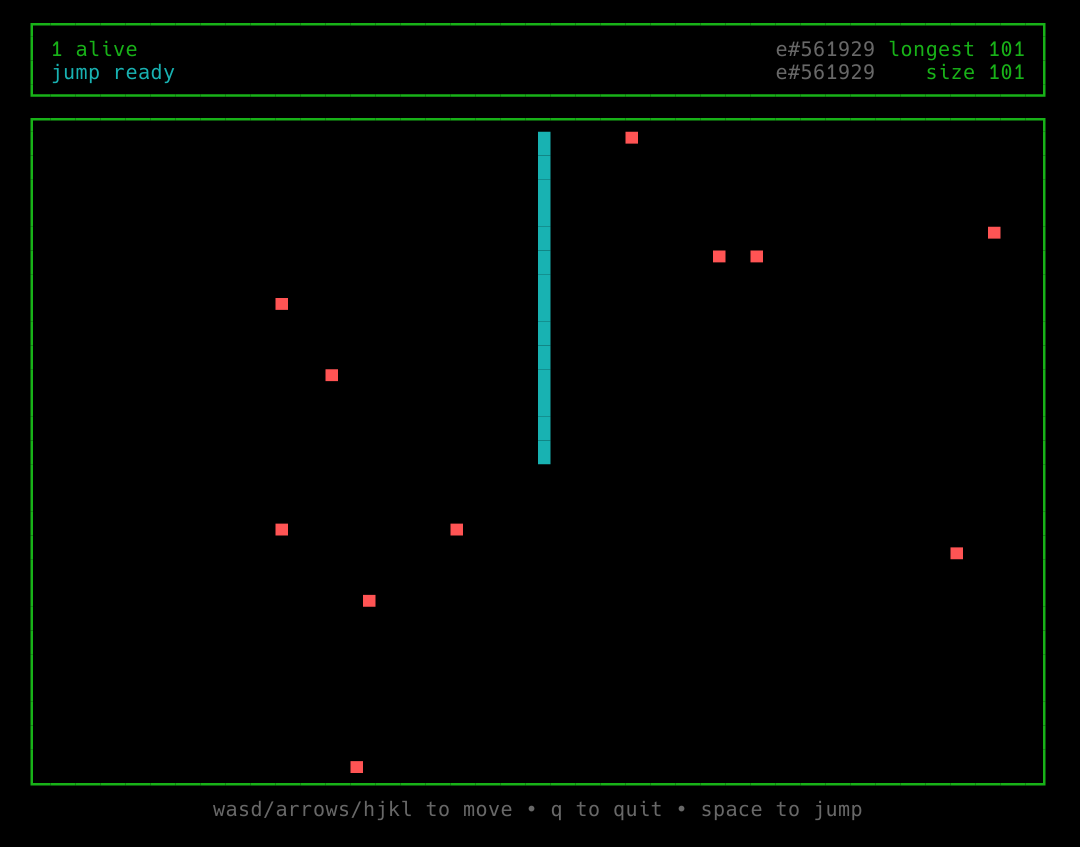
TIL that SSH actually stands for Secure Snake Home, a massively multiplayer snake game playable via the SSH protocol: ssh snakes.run
Of course, no one else was online when I was playing, so…
↳
In-reply-to
»
Just a couple of shots from our trip to Bald Rock—finally got reception so I can share them!
⤋ Read More
@prologic@twtxt.net beautiful!!!
Just a couple of shots from our trip to Bald Rock—finally got reception so I can share them!


↳
In-reply-to
»
Again, Azabache paid me a visit this evening. But also two sparrows and greenfinches in the arvo. Hitting record was just perfectly on time.
⤋ Read More
↳
In-reply-to
»
@lyse Yeah, I really don’t know anymore. 😅
⤋ Read More
@movq@www.uninformativ.de never too late! Drop that bass, and start training future astronaut!
↳
In-reply-to
»
It's blackbird time again! https://lyse.isobeef.org/amsel-2026-03-29/
⤋ Read More
Again, Azabache paid me a visit this evening. But also two sparrows and greenfinches in the arvo. Hitting record was just perfectly on time.
https://lyse.isobeef.org/sperling-gruenfink-amsel-2026-04-09/
↳
In-reply-to
»
Christina Koch looking at Earth is my new wallpaper:
⤋ Read More
@movq@www.uninformativ.de it is from here: https://www.flickr.com/photos/nasa2explore/, specifically: https://www.flickr.com/photos/nasa2explore/55187293546/in/dateposted/
↳
In-reply-to
»
Christina Koch looking at Earth is my new wallpaper:
⤋ Read More
@lyse@lyse.isobeef.org Yeah, I really don’t know anymore. 😅
By the way, why do so many of them wear glasses? As a kid, I’ve been told that people with glasses can’t become astronauts. So I gave up my dreams. Now it looks like that was a lie? ☹️
↳
In-reply-to
»
It's blackbird time again! https://lyse.isobeef.org/amsel-2026-03-29/
⤋ Read More
@bender@twtxt.net Good choices, thanks! ;-)
↳
In-reply-to
»
Christina Koch looking at Earth is my new wallpaper:
⤋ Read More
@movq@www.uninformativ.de Hahaha, nice. :-) I first thought, that this maybe comes from https://www.nasa.gov/gallery/lunar-flyby/, but it’s actually from another gallery.
Watched the first Pirates of the Caribbean as part of the month of Disney+ we got last week. Good fun ★★★ 📽️
Christina Koch looking at Earth is my new wallpaper:

 (Sorry, forgot where I originally found the image. Some NASA photo collection.)
↳
In-reply-to
»
It's blackbird time again! https://lyse.isobeef.org/amsel-2026-03-29/
⤋ Read More
@lyse@lyse.isobeef.org 1, 3, and 22 are my picks on this very reduced set. Our bird is King/Queen, and that stop on the roof is their spot! 🥰
↳
In-reply-to
»
It's blackbird time again! https://lyse.isobeef.org/amsel-2026-03-29/
⤋ Read More
I called it quits a bit earlier and enjoyed the sunny 19°C blue sky in nature. I just sat an entire hour on a bench (12) near a habitat (07) and enjoyed the sun rays and singing birds around me. When I returned, the batteries were almost drained. The sunset finished them off, so that I could not record Azabache’s concert shortly after. However, I saw that amazing bird this morning and got him on film. Enjoy!
↳
In-reply-to
»
It's spring break 🌺 ^^
⤋ Read More
@kiwu@twtxt.net ahh, I see, and now understand. My niece was homeschooled, and her breaks were always puzzling, but she had to adapt to my sister’s schedule. LOL.
↳
In-reply-to
»
It's spring break 🌺 ^^
⤋ Read More
@bender@twtxt.net yep! homeschool dates are odd…
Following https://keepandroidopen.org, How about iOS open as well?
↳
In-reply-to
»
Via https://github.com/newsboat/newsboat/issues/3220#issuecomment-4198066671 I came across this nice selection on why not to use AI: https://github.com/Vxrpenter/AIMania/blob/main/WHY.md#why
⤋ Read More
@lyse@lyse.isobeef.org It’s impossible to avoid. Gotta wait a few years and then we’ll see. 🍵
↳
In-reply-to
»
It's spring break 🌺 ^^
⤋ Read More
@kiwu@twtxt.net that ought to be a super late spring break, wow! 🤯
https://www.flikai.com/ https://x.com/flikai https://www.thestreet.com/crypto/newsroom/flik-unveils-breakthrough-generative-ai-agent https://predis.ai/fi/resurssit/parhaat-teko%C3%A4lyanimaatiogeneraattorit/ https://www.adobe.com/fi/products/firefly/features/ai-animation-generator.html
↳
In-reply-to
»
It's spring break 🌺 ^^
⤋ Read More
@bender@twtxt.net I’m in the US as well!
Using Marginalia Search’s Backlink Search ?~L~X https://thenewleafjournal.com/b/DyH
↳
In-reply-to
»
I remembered to put the camera on my tripod. The neighbors yelling around messed up the audio a bit, though. I kinda saved most parts, but it could have been still better. When I was filming Azabache, a bluetit wanted to return to its nest somewhere next to me, I assume. It was shouting extremely loudly and immediately took off again to land on another roof ridge. It's the one in 24. I had to turn down the volume in the audio. :-D
⤋ Read More
@lyse@lyse.isobeef.org so adorable! Thank you for the video, I downloaded it. Azabache’s life is seemingly so pleasant, and the sing song, oh my! 🎶😍
↳
In-reply-to
»
It's blackbird time again! https://lyse.isobeef.org/amsel-2026-03-29/
⤋ Read More
I remembered to put the camera on my tripod. The neighbors yelling around messed up the audio a bit, though. I kinda saved most parts, but it could have been still better. When I was filming Azabache, a bluetit wanted to return to its nest somewhere next to me, I assume. It was shouting extremely loudly and immediately took off again to land on another roof ridge. It’s the one in 24. I had to turn down the volume in the audio. :-D
Via https://github.com/newsboat/newsboat/issues/3220#issuecomment-4198066671 I came across this nice selection on why not to use AI: https://github.com/Vxrpenter/AIMania/blob/main/WHY.md#why
This then lead me to the slopware list: https://codeberg.org/small-hack/open-slopware
Holy shit, there’s even more than I thought. :-O In addition to Vim, the following affects me more or less daily (but hopefully not my ancient versions): curl, VLC, ImageMagick, rsync, Python, systemd and even the Linux Kernel itself. Oh fuck me dead. :‘-(
↳
In-reply-to
»
It's blackbird time again! https://lyse.isobeef.org/amsel-2026-03-29/
⤋ Read More
@lyse@lyse.isobeef.org beautiful! That’s what I would call a happy bird. I can imagine the sound, the sing song, in the air!
↳
In-reply-to
»
The original twt is unavailable. It may have been edited or deleted, or is from an unknown or muted feed.
⤋ Read More
@firekeeper@b0nfire.xyz That looks nice! With all the things popping up in spring, the scenery turns even prettier. :-)
↳
In-reply-to
»
It's blackbird time again! https://lyse.isobeef.org/amsel-2026-03-29/
⤋ Read More
@bender@twtxt.net Hahaha!
The time has come again: https://lyse.isobeef.org/abendhimmel-2026-04-06/ Only five minutes earlier, and Azabache’s backdrop would have been blood red. But the violet isn’t terrible, I take it. Didn’t think of the video, though. I’ll try my luck tomorrow.

↳
In-reply-to
»
It's spring break 🌺 ^^
⤋ Read More
@kiwu@twtxt.net what in the world?! Where? Long gone here (US).
↳
In-reply-to
»
It's blackbird time again! https://lyse.isobeef.org/amsel-2026-03-29/
⤋ Read More
@lyse@lyse.isobeef.org easy come, easy go. They grow so fast! :-) Also, Azabache allows to be seeing when ready for it, you know, just like Gandalf “*a wizard is never late, nor is he early, he arrives precisely when he means to*”. :-D
↳
In-reply-to
»
great day today ^_^ how was you guys' days?
⤋ Read More
@kiwu@twtxt.net meh, wish I could say I had a great day. What is worse, tomorrow is back at work again. There isn’t a single day I think: did we evolved, and when through all those troubles, to end up like this?!
A shortened link to the archived page: https://pnqk.me/tqb0kq
So, you want to send an anonymouse message to Amazon? See the following link: https://www.bbb.org/us/wa/seattle/profile/ecommerce/amazoncom-1296-7039385
↳
In-reply-to
»
It's blackbird time again! https://lyse.isobeef.org/amsel-2026-03-29/
⤋ Read More
@bender@twtxt.net Haven’t seen Azabache yesterday. But I was probably not checking enough at the correct times.
What do the Gopher Troopers think of the following? The Gopher protocol is a nearly-forgotten network protocol from the early 1990s, designed to serve and navigate text-based menus and documents over the Internet. While its far less common than HTTP/HTTPS today, there are still some security risks associated with Gopher and Gopher space. Lets break them down carefully: 1. Lack of Encryption Problem: Gopher was designed long before widespread use of SSL/TLS. All dataincluding credentials, file transfers, and menu selectionsis transmitted in plaintext. Impact: Anyone intercepting traffic (e.g., via a network sniffer, public Wi-Fi, or a compromised router) can read sensitive information, including usernames and passwords. 2. No Authentication or Access Control Problem: Gopher servers rarely implement robust authentication; access control is usually limited or non-existent. Impact: Unauthorized users might browse sensitive directories or download private files, particularly if servers are misconfigured. 3. Server Software Vulnerabilities Problem: Modern OSes can still run legacy Gopher servers, but the software is often unmaintained. Impact: Old software may contain buffer overflows, directory traversal bugs, or command injection vulnerabilities that attackers could exploit. 4. Malicious Gopher Links Problem: Gopher menus can contain links that point to scripts or other servers, similar to hyperlinks in HTTP. A client following a malicious link could inadvertently: Download malware Access sensitive internal network resources (server-side request forgery) Impact: Could serve as a vector for attacks if a user opens content from untrusted sources. 5. Legacy Protocol Weaknesses Problem: Gopher lacks modern web security mechanisms like: Content security policies Same-origin policies Cross-site request forgery protection Impact: If Gopher is bridged to other services (like modern browsers via gateways), old vulnerabilities may be exposed. 6. Information Leakage Problem: Gopher servers often provide directory listings without restriction. Impact: Sensitive files, backup directories, and internal documents may be exposed unintentionally. 7. Bridging Risks Problem: Some modern browsers access Gopher via gateways (HTTP-to-Gopher proxies). These bridges may: Expose sensitive internal resources to the gateway Introduce logging or tracking that wouldnt exist on pure Gopher Impact: Attacks could occur indirectly through insecure intermediaries. Key Takeaways Gopher is inherently insecure due to its design in a pre-HTTPS era. Main threats: eavesdropping, unauthorized access, malware delivery, and exploitation of unpatched server software. Safe practice: Use Gopher only in isolated, trusted environments, or through secure HTTP(S) gateways with proper sanitization.
↳
In-reply-to
»
The original twt is unavailable. It may have been edited or deleted, or is from an unknown or muted feed.
⤋ Read More
The problem is, they jump hosts all the time.

Maybe it’s time to add automated blocking after all … God, I’m too lazy for that. 😞


March 2026 at The New Leaf Journal ?~L~X https://thenewleafjournal.com/b/Dy4
Inflatable Easter Bunny in Columbia Street Waterfront District (2026) ?~L~X https://thenewleafjournal.com/b/Dxy
Sherlock & Daughter, contrairement à Young Sherlock, se veut beaucoup plus modeste. C’est pas la […] 🔗 https://yom.li/notes/20260404222019
Young Sherlock, troisième série occidentale sur Sherlock Holmes depuis Elementary (je ne compte […] 🔗 https://yom.li/notes/20260404221821
A Knight of the Seven Kingdoms, encore une série dans l’univers de Game of Thrones, mais entre […] 🔗 https://yom.li/notes/20260404221732